Clicxpost

Tech

2 South Carolina police officers fired for misusing Flock cameras, city officials say

Greer police officers fired

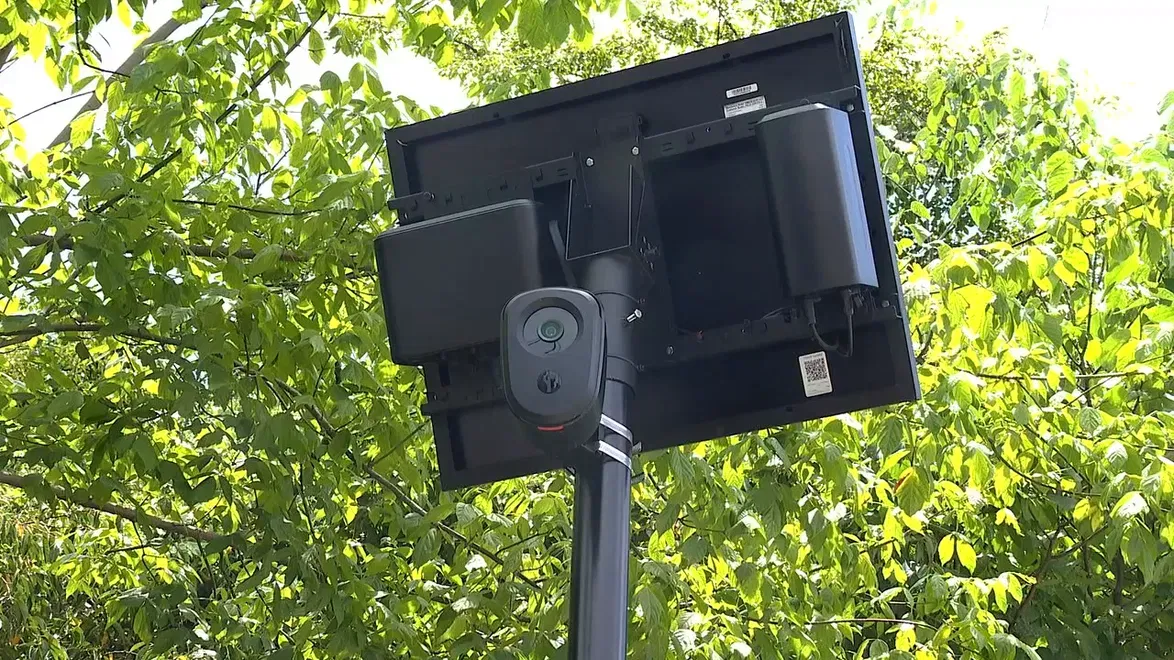
Two police officers in Greer, South Carolina have lost their jobs after an internal audit found they misused the department’s automatic license plate reader technology.

The Greer Police Department’s policy on Flock Safety cameras requires the AI-powered license plate readers to be used only for what the department calls public safety related missions. Any violation of that policy can bring disciplinary action, according to a press release from the City of Greer. The city said the policy has gone through multiple revisions, with updated versions distributed to staff each time.

How the misuse was discovered

The department began investigating after receiving allegations that two officers were violating the camera policy. To check the claims, Greer police used Flock Safety’s AI Audit Assistance tool, a system built to review how officers are querying the license plate database.

City Administrator Andrew Merriman said the audit backed up what investigators had been told. “The audit corroborated the initial information, and as a result, the two officers were terminated,” Merriman said in the release. “The City of Greer takes seriously the responsibility to protect the life, safety, and privacy of our citizens, and we utilize the latest tools and technology to perform those duties.”

Corporal Kareem Lynch was terminated June 26. Officer Sebastian Echeverry was terminated three days later, on June 29. The department has reported both terminations to the South Carolina Criminal Justice Academy, which will determine whether the officers keep their law enforcement certifications.

What Flock cameras do
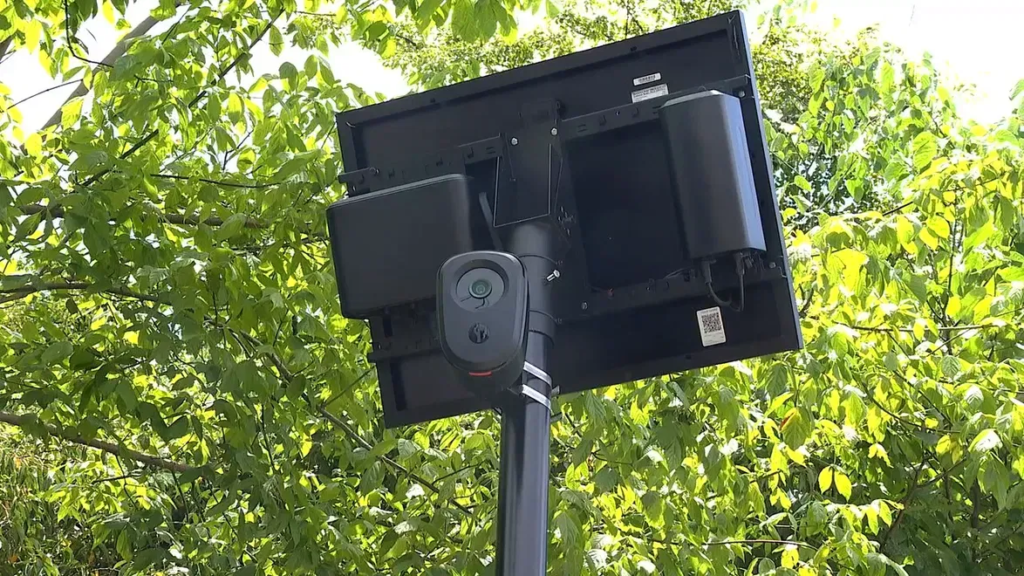
Flock Safety’s cameras read license plates and flag matches against databases of stolen vehicles, wanted suspects, and other law enforcement alerts. Police departments across the country have adopted the technology over the past several years as a tool for locating suspect vehicles quickly, but the systems have also drawn scrutiny over how much access individual officers have to search historical plate data, and what stops them from using that access for reasons unrelated to an active investigation.

The audit tool Greer used represents a newer layer added to that scrutiny: rather than relying solely on internal complaints or manual log reviews, Flock’s AI system can flag unusual search patterns for a department to investigate on its own.

A broader debate over the technology

Greer’s case lands in the middle of a wider conversation happening in South Carolina and beyond about how license plate readers should be governed. Some residents and local officials have raised concerns about the privacy implications of a camera network capable of tracking vehicle movements over time, while law enforcement agencies argue the tool helps them solve crimes and locate missing people faster than traditional methods allow.

That tension has played out in neighboring communities as well, where local governments have held public discussions weighing the safety benefits of the cameras against concerns about surveillance overreach. The debate tends to center less on whether the technology works and more on who can access the data it collects, for what purposes, and how departments enforce those limits once the cameras are installed.

Greer’s decision to terminate two officers over policy violations, rather than simply issue a warning or retraining, signals how seriously the department is treating that access question. Merriman’s statement framed the terminations explicitly around protecting citizen privacy, not just correcting a procedural lapse.

What happens next

With the case now referred to the state’s Criminal Justice Academy, the outcome for Lynch and Echeverry extends beyond their employment status in Greer. The Academy’s review will determine whether either officer can continue working in law enforcement elsewhere in South Carolina, since certification decisions made at the state level typically affect an officer’s ability to be hired by any other department in the state.

Neither the specific nature of the officers’ alleged misuse nor additional details from the audit were included in the city’s release. The department has not said whether the queries in question were tied to personal matters, unauthorized information requests, or another form of policy violation, and it’s unclear whether any criminal charges are being considered alongside the certification review.

The case adds to a growing list of incidents nationally in which police departments have disciplined or fired officers for misusing license plate reader systems, as more agencies adopt the technology and build out auditing tools capable of catching violations that might previously have gone unnoticed. For Greer, the terminations mark an early test of how the department’s revised camera policy holds up in practice, and whether the disciplinary response is enough to reassure residents concerned about how the surveillance tool is being used.
RECOMMENDED
Tech

Bill Gates Warns AI and Robots Will Take Jobs in Offices and Manual Work

By George Mensah 7 min read

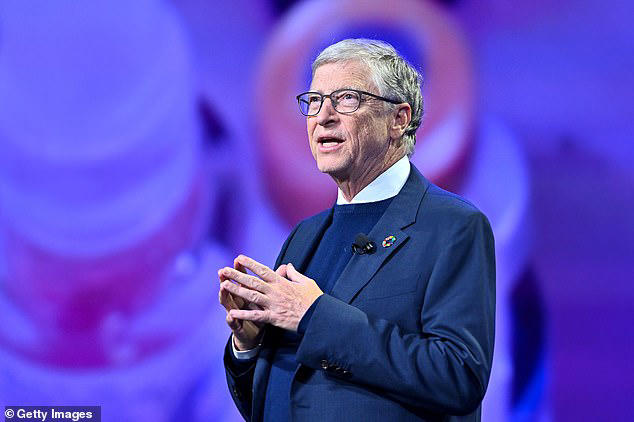
Bill Gates has warned that artificial intelligence and humanoid robots will take jobs in offices and in manual trades, and that company profit targets will push the change forward faster than governments can prepare for it.

The Microsoft founder made the comments in an interview with The Observer. He said that “skills of invention, skills of white-collar work and then with humanoids, the skills of physical human labour” could all be replaced by AI. In his view, no category of work is safe from the technology for long.

The warning follows a job-cut announcement from Barclays and a blunt assessment from the head of the International Monetary Fund, both made last week. It also comes just ahead of the first Budget from UK Chancellor John Healey, who is expected to commit millions of pounds to AI safety.

“Hire the robot, fire the human”

Gates did not put the blame on the machines. He put it on what businesses are paid to do. He described an “incentive structure” in which companies looking to raise profits have every reason to swap people for software or hardware.

“It’s hire the robot, fire the human and don’t look back,” he said.

That reasoning explains why the pace of change may not depend on how good the technology gets. If a robot costs less than a salary and does the task acceptably, a finance director has a clear reason to choose it, whatever the effect on the workforce.

AI has already been costing jobs for several years. Office work has taken the first hits, particularly data-driven analytical roles. Software development, data entry and customer service have all lost positions as companies have found that AI tools can handle parts of that work at a fraction of the cost of a person.

Barclays cuts 5,000 jobs

The most recent example came from banking. Last week Barclays announced that it would replace 5,000 jobs with AI by the end of the year, with cost reduction as the stated aim.

The bank said the cuts amount to 5 per cent of its global workforce. That figure implies a total headcount of around 100,000 people, so one in every twenty employees is affected. The timetable matters as much as the number. Cutting a twentieth of a workforce within a few months leaves little room for retraining or gradual attrition.

Barclays framed the move as a way to cut costs, which matches the motive Gates described. The stated reason is price, and price is the incentive Gates described.

The IMF’s “slow-moving tsunami”

The same week, the head of the International Monetary Fund described AI as “a slow-moving tsunami” that would wipe out jobs around the world. Kristalina Georgieva singled out young people as the group with the most to lose.

Her reasoning is specific. Entry-level jobs have traditionally been filled by people with little experience, and they tend to involve routine, repeatable tasks. The IMF chief said AI already does that kind of menial work well and at very little cost.

The IMF has framed the shift as slow but steady, so the damage may build up quietly before it becomes visible in unemployment figures. Those jobs also served a second purpose. They gave graduates and school leavers a first rung on a career, and a place to learn how an organisation runs. If employers stop hiring for them, a generation of workers could find that the way into a profession has narrowed before they reach it. Nobody has yet shown what replaces that route.

Governments face a money problem

Gates said governments would need to adapt to cope with mass unemployment, mainly through education and re-skilling.

He also pointed to a difficulty that sits inside the argument for AI itself. The technology is likely to bring more “prosperity”, he said, but governments would still have less money to deal with the fallout from huge job losses. Fewer workers means fewer people paying income tax and national insurance, even if company profits rise.

He added that these demands would land when states already have competing priorities and geopolitical tensions are rising.

“You could say this isn’t the best time to say, ‘Hey, rich countries, let’s do the hardest thing you’ve ever done’,” he said.

The comment is a frank admission from someone who has spent decades arguing for technology’s benefits. Gates is not saying that rich countries cannot respond. He is saying that the moment when they must respond is a poor one.

AI beyond human control

Gates went further than employment. He argued that AI could soon overtake humans as the most intelligent things on the planet.

He also predicted that by the end of the 2020s, AI could be operating beyond human control. In that situation, he warned, the technology could act against human interests. The reported remarks do not say how or why that might happen.

A former insider’s warning

A younger voice from inside the industry has made a similar case. Jacob Coxon, 27, helped train the latest versions of AI at the San Francisco-based company Anthropic, which makes the Claude system. He previously worked at OpenAI, the company behind ChatGPT.

Coxon urged people to “not underestimate” the power of AI, particularly if it becomes “super-intelligent”. He also claimed that neither Anthropic nor OpenAI was “acting responsibly” over AI safety.

Superintelligence is the point at which an artificial system becomes more powerful than any individual, company or even nation. The claim about both firms comes from Coxon alone. The article has not seen a response from either company, and readers should treat his statement as one person’s assessment, not an established finding.

The Budget response

The UK government is preparing its answer. Chancellor John Healey is expected to commit millions of pounds in next week’s Budget to guard against the risks of AI, while also aiming to use the technology for economic advantage across the country.

Ahead of his maiden statement on Wednesday, Healey said AI would “transform daily life”. He added that “every firm, community, hospital, school and every aspect of our economy” could benefit from it.

He also acknowledged the worry about jobs. Healey said he understood growing concerns that AI would take away people’s work, which was why he would be “setting out a distinctively British approach to AI – one that doesn’t leave workers behind and defends our national interest, while ensuring the benefits of AI-enabled growth are felt right across the country”.

The pledge sets a high bar. Gates has just argued that governments will have less money to cushion job losses, and Barclays has just shown how fast a large employer can move. A promise not to leave workers behind will be judged on the size of the budget behind it and on what the Treasury is prepared to spend on retraining.

£300 million for a biosecurity lab

The government will also spend £300 million backing an AI Biosecurity Lab. The lab will look at protections from emerging biological threats.

It will be a public-private partnership supported by AI developers including OpenAI and Anthropic. The same companies whose products are blamed for rising job losses, and which Coxon says are not acting responsibly on safety, will therefore sit inside a publicly funded safety project. Whether that arrangement gives the government real independence over the lab’s work is a question the Budget papers should answer.

What is known and what is a forecast

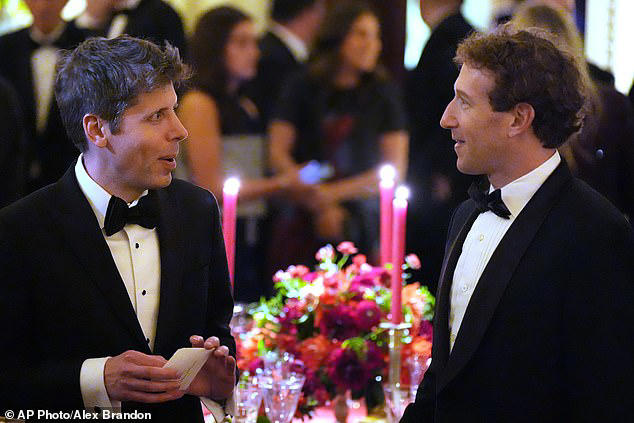
OpenAI CEO Sam Altman talks with Meta CEO Mark Zuckerberg in September 

Some of the claims in this story are facts and some are predictions, and they should be read differently. The Barclays cuts, the 5 per cent figure and the £300 million biosecurity lab are announced decisions with numbers attached. The IMF’s “tsunami” and Gates’s timeline for AI slipping beyond human control are forecasts. Coxon’s criticism of Anthropic and OpenAI is an opinion from a former employee.

For workers in the roles already named, the practical picture is narrower than the headlines. Data entry, customer service and software development are where cuts have been reported so far. The manual-labour warning depends on humanoid robots reaching workplaces at scale, and Gates gave no date for that.

What to watch next

Three things will show how seriously the government takes these warnings. The first is the Budget itself, where the AI safety figure and any money for retraining will be visible in the numbers. The second is the detail on the biosecurity lab, including who sets its priorities. The third is whether more large employers follow Barclays and put a number and a date on AI-driven job cuts.

Gates, Georgieva and Healey have each described the same risk in different terms. Gates and Georgieva say the jobs are at risk now. Healey says the benefits can reach everyone. Next week’s Budget will show how much public money the Chancellor is willing to put behind that claim.

Tech

What is PHP and why did it take government websites offline?

By George Mensah 5 min read

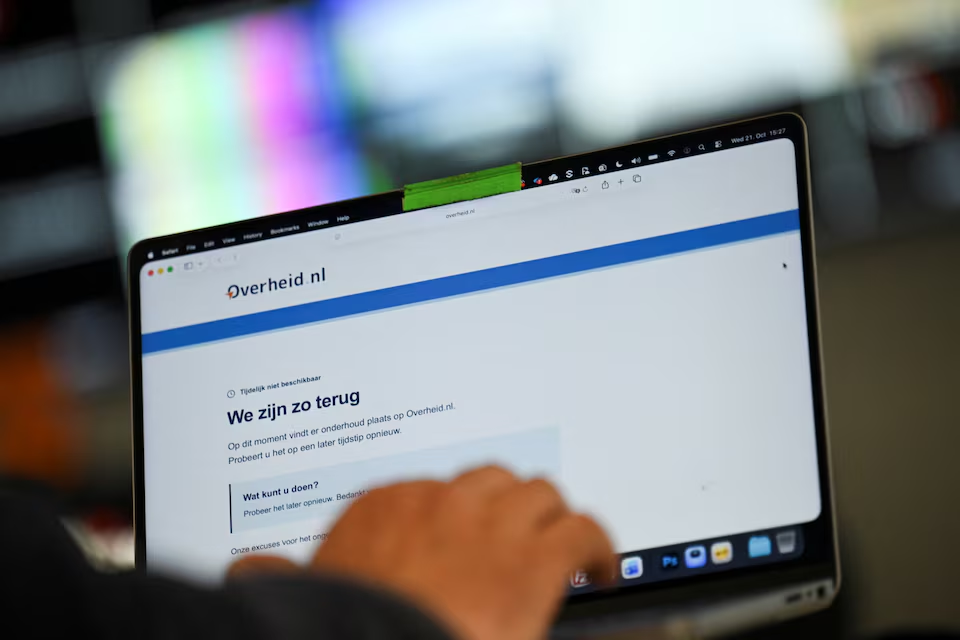
Government websites across Europe went dark on Wednesday as operators rushed to patch two critical vulnerabilities in PHP, one of the most widely used programming languages on the web. The developers of PHP said the same day that they would release patches for both flaws. EU cybersecurity officials warned that organisations unable to apply the fixes should take affected websites offline.

The flaws carry a severity score of 9.2 out of 10. An attacker who exploits either one can run commands on a vulnerable server over the internet, with no password and no account. The chief technology officer of Cloudflare said early attacks were already emerging.

If you run a website, the first question is whether your host has applied the fix. The usual automatic updates will not do it for you, according to a warning from Wordfence, the WordPress security plugin maker.

What PHP Is

PHP is a programming language that runs websites from behind the scenes. When someone loads a page, the server running PHP assembles the content and sends the finished page to the browser. It is free, open source and maintained by volunteers, and site owners rarely deal with it directly.

The web technology tracker W3Techs reports that PHP runs nearly 70 percent of all websites whose programming language can be identified. It is also the engine behind WordPress, the software that powers about 40 percent of all websites. Blogs, small business pages, government portals, online shops and news sites all run on it.

The two figures explain why one bug can reach so many places. A flaw in PHP does not affect one product or one company. It affects every server running the vulnerable code.

How Serious the Flaws Are

Cyber agencies warn that websites may be taken offline while PHP prepares a critical fix

Both vulnerabilities are rated 9.2 out of 10 on the CVSS v4.0 scale, a standard industry scoring system. CERT-EU, the European Union’s cybersecurity response team, said the rating signals unauthenticated remote code execution. In plain terms, an attacker can run commands on a vulnerable server, over the internet, without logging in.

Whoever exploits the flaw controls the website. GoDaddy, the web hosting provider, said that could mean stolen data, defaced pages or full-system compromise.

A single flaw in PHP opens the same door on millions of servers at once, which is why attackers move fast once details become public. Cloudflare’s chief technology officer said early attacks were emerging, so the window for patching is already narrowing.

Why Small Sites Face the Biggest Risk

Most small websites are run by owners with no security staff. Many sit on shared hosting, where the owner does not manage the server and may not know who updates PHP.

Wordfence warned that the automatic updates WordPress users normally rely on will not apply this fix. The patch has to be installed on the server, which is the host’s job. CERT-EU’s guidance is direct: if an affected site cannot be fixed, take it offline instead of leaving it exposed.

That advice explains the European government outages. Taking a site down costs visitors and services for a while, but it removes the target.

How the Flaws Were Found

Cyber agencies warn that websites may be taken offline while PHP prepares a critical fix

Researchers at the security firm Calif, working with OpenAI, reported the first flaw to PHP on August 11. They found it with OpenAI’s GPT-5.6 Sol model, the company said.

Wiz, a security firm owned by Alphabet’s Google, found the flaws independently and reported a second one on August 24, also using AI models.

By the dates given, the first report reached PHP 71 days before Wednesday’s announcement, and the second reached it 58 days before. That is about ten weeks and eight weeks of work between report and patch release. The reporting does not say how much of that time went to building the fixes and how much to testing them.

An Old Bug That Needed a Long Chain

Wiz said the findings “rank among the most severe vulnerabilities discovered in PHP, and arguably in software history.” The underlying flaws had been present for decades, the firm said. Proving they were exploitable, however, required a chain of steps “at the edge of what human researchers could practically achieve.”

That second point is the new element. Two separate teams, each using AI models, found bugs that had survived years of human review. Wiz’s own description is that the exploit chain sat at the limit of what people could do unaided.

Washington Frames It as a Win for AI

The administration of US President Donald Trump said it was “tracking and coordinating with federal agencies and leading SI labs to expedite the release of the fix.” “SI” is the administration’s preferred name for artificial intelligence. It presented the discovery as evidence that American “Super Intelligence” strengthens national security.

The statement treats the finding as a success, and the vulnerabilities as a problem solved by the same technology. The reporting so far confirms the first part, since AI tools found the flaws. It does not yet show the second, because the reporting does not confirm that the patches are out.

What You Should Do

The guidance below follows the warnings from CERT-EU, Wordfence and GoDaddy. Check the details with your own host.

  • Ask your host. If you use shared hosting, contact your provider and ask whether the PHP fix has been applied to your server. You cannot patch it yourself.
  • Do not count on automatic updates. Wordfence said the usual WordPress updates will not apply this fix.
  • Consider taking the site offline. If your host cannot confirm a fix, CERT-EU recommends removing the site from the internet until it is patched.
  • Back up your data first. A copy of your files and database lets you recover if the site is defaced or damaged.
  • Watch for changes. Unexpected pages, new admin accounts or files you did not upload can be signs of a compromise.

If you run your own server, install the PHP patch as soon as it is released.

What Remains Unclear

The reports leave several questions open. PHP’s developers said they would release patches, but the reporting does not say whether they are out or give a release date. It does not name the affected PHP versions or give the identifiers assigned to the two flaws. It does not say how many servers are exposed or how many have already been attacked. Cloudflare’s chief technology officer said early attacks were emerging, but no number or target was given.

Three things will show how this plays out. The first is the release of the patches. The second is how quickly hosting providers apply them. The third is whether the attacks Cloudflare described grow once the fix details become public.

Sources

ADVERTISEMENT
Scroll to Top