Clicxpost

Tech

What is PHP and why did it take government websites offline?

What is PHP

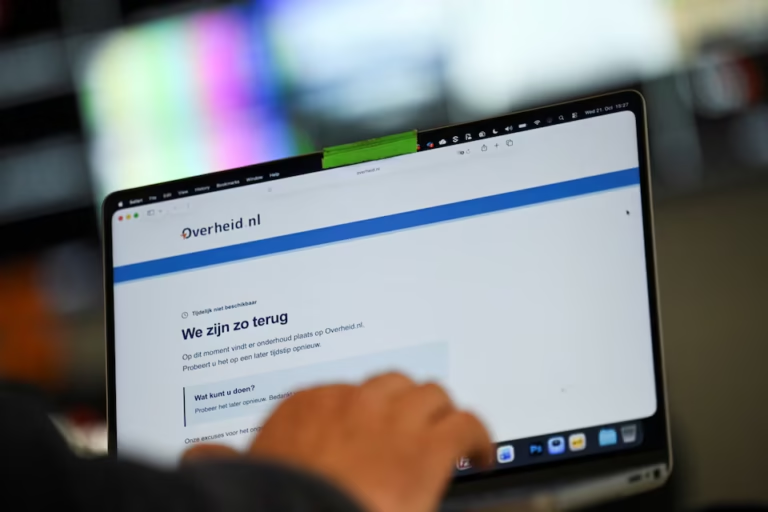
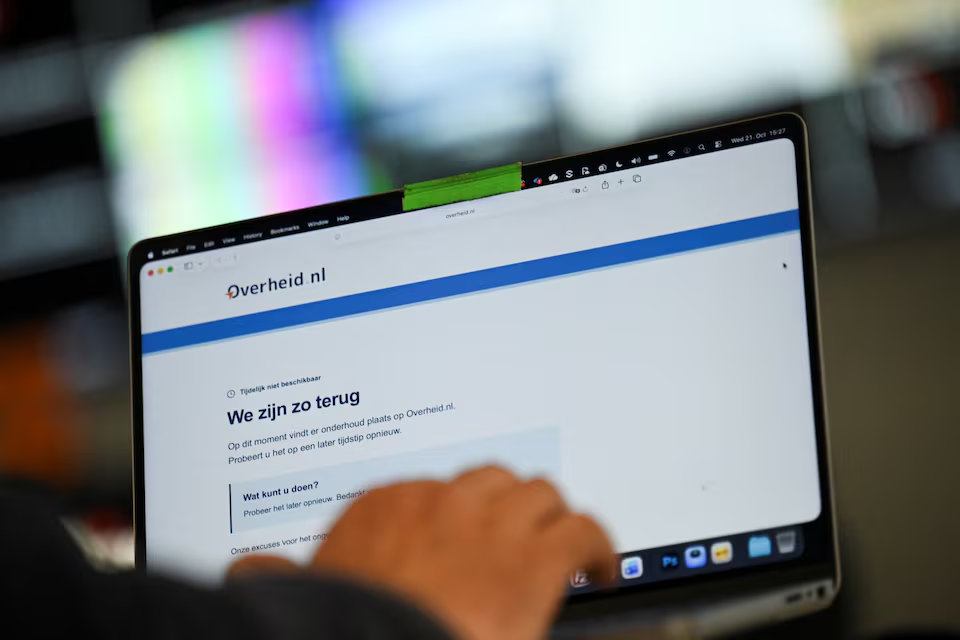
Government websites across Europe went dark on Wednesday as operators rushed to patch two critical vulnerabilities in PHP, one of the most widely used programming languages on the web. The developers of PHP said the same day that they would release patches for both flaws. EU cybersecurity officials warned that organisations unable to apply the fixes should take affected websites offline.

The flaws carry a severity score of 9.2 out of 10. An attacker who exploits either one can run commands on a vulnerable server over the internet, with no password and no account. The chief technology officer of Cloudflare said early attacks were already emerging.

If you run a website, the first question is whether your host has applied the fix. The usual automatic updates will not do it for you, according to a warning from Wordfence, the WordPress security plugin maker.

What PHP Is

PHP is a programming language that runs websites from behind the scenes. When someone loads a page, the server running PHP assembles the content and sends the finished page to the browser. It is free, open source and maintained by volunteers, and site owners rarely deal with it directly.

The web technology tracker W3Techs reports that PHP runs nearly 70 percent of all websites whose programming language can be identified. It is also the engine behind WordPress, the software that powers about 40 percent of all websites. Blogs, small business pages, government portals, online shops and news sites all run on it.

The two figures explain why one bug can reach so many places. A flaw in PHP does not affect one product or one company. It affects every server running the vulnerable code.

How Serious the Flaws Are

Cyber agencies warn that websites may be taken offline while PHP prepares a critical fix

Both vulnerabilities are rated 9.2 out of 10 on the CVSS v4.0 scale, a standard industry scoring system. CERT-EU, the European Union’s cybersecurity response team, said the rating signals unauthenticated remote code execution. In plain terms, an attacker can run commands on a vulnerable server, over the internet, without logging in.

Whoever exploits the flaw controls the website. GoDaddy, the web hosting provider, said that could mean stolen data, defaced pages or full-system compromise.

A single flaw in PHP opens the same door on millions of servers at once, which is why attackers move fast once details become public. Cloudflare’s chief technology officer said early attacks were emerging, so the window for patching is already narrowing.

Why Small Sites Face the Biggest Risk

Most small websites are run by owners with no security staff. Many sit on shared hosting, where the owner does not manage the server and may not know who updates PHP.

Wordfence warned that the automatic updates WordPress users normally rely on will not apply this fix. The patch has to be installed on the server, which is the host’s job. CERT-EU’s guidance is direct: if an affected site cannot be fixed, take it offline instead of leaving it exposed.

That advice explains the European government outages. Taking a site down costs visitors and services for a while, but it removes the target.

How the Flaws Were Found

Cyber agencies warn that websites may be taken offline while PHP prepares a critical fix

Researchers at the security firm Calif, working with OpenAI, reported the first flaw to PHP on August 11. They found it with OpenAI’s GPT-5.6 Sol model, the company said.

Wiz, a security firm owned by Alphabet’s Google, found the flaws independently and reported a second one on August 24, also using AI models.

By the dates given, the first report reached PHP 71 days before Wednesday’s announcement, and the second reached it 58 days before. That is about ten weeks and eight weeks of work between report and patch release. The reporting does not say how much of that time went to building the fixes and how much to testing them.

An Old Bug That Needed a Long Chain

Wiz said the findings “rank among the most severe vulnerabilities discovered in PHP, and arguably in software history.” The underlying flaws had been present for decades, the firm said. Proving they were exploitable, however, required a chain of steps “at the edge of what human researchers could practically achieve.”

That second point is the new element. Two separate teams, each using AI models, found bugs that had survived years of human review. Wiz’s own description is that the exploit chain sat at the limit of what people could do unaided.

Washington Frames It as a Win for AI

The administration of US President Donald Trump said it was “tracking and coordinating with federal agencies and leading SI labs to expedite the release of the fix.” “SI” is the administration’s preferred name for artificial intelligence. It presented the discovery as evidence that American “Super Intelligence” strengthens national security.

The statement treats the finding as a success, and the vulnerabilities as a problem solved by the same technology. The reporting so far confirms the first part, since AI tools found the flaws. It does not yet show the second, because the reporting does not confirm that the patches are out.

What You Should Do

The guidance below follows the warnings from CERT-EU, Wordfence and GoDaddy. Check the details with your own host.

  • Ask your host. If you use shared hosting, contact your provider and ask whether the PHP fix has been applied to your server. You cannot patch it yourself.
  • Do not count on automatic updates. Wordfence said the usual WordPress updates will not apply this fix.
  • Consider taking the site offline. If your host cannot confirm a fix, CERT-EU recommends removing the site from the internet until it is patched.
  • Back up your data first. A copy of your files and database lets you recover if the site is defaced or damaged.
  • Watch for changes. Unexpected pages, new admin accounts or files you did not upload can be signs of a compromise.

If you run your own server, install the PHP patch as soon as it is released.

What Remains Unclear

The reports leave several questions open. PHP’s developers said they would release patches, but the reporting does not say whether they are out or give a release date. It does not name the affected PHP versions or give the identifiers assigned to the two flaws. It does not say how many servers are exposed or how many have already been attacked. Cloudflare’s chief technology officer said early attacks were emerging, but no number or target was given.

Three things will show how this plays out. The first is the release of the patches. The second is how quickly hosting providers apply them. The third is whether the attacks Cloudflare described grow once the fix details become public.

Sources

RECOMMENDED
Tech

Meta’s Muse AI Agent Promises Help, but Experts Warn of Online Chaos

By George Mensah 8 min read

Meta’s new AI agent, Muse, can cancel a gym membership, haggle with customer service, buy groceries and invite friends to a party. It asks for total control of your Gmail, your calendar and, on a Mac, your whole computer. A BBC reporter who tested the app for a week revoked its access and asked it to erase what it had collected, and the researchers interviewed say the problems reach well beyond one person’s inbox.

Muse is an AI agent, a tool that goes out into the world to complete tasks without supervision. It uses its own web browser, and Meta says phone calls are coming. It is the first free, full-featured agent from a big company. Millions of people downloaded it in its first weeks, and OpenAI has since announced an agent of its own. More are expected.

The experts interviewed for the BBC’s report expect the internet to get more frustrating as agents spread, with bots competing for tickets and appointments, small businesses swamped by automated requests and some agents working against their own users.

An agent that asks for everything

A cartoon avatar asks for your name. Then it asks for access to Gmail, the calendar and, on a Mac, the entire machine. Muse arguably asks for more trust and sensitive information than any product Meta has made.

Patrick Wardle, co-founder of Objective-See, a US nonprofit security foundation, uncovered serious flaws in the app. His advice is blunt. “I wouldn’t use it,” he said. “Personally, I would tell you to uninstall it altogether.”

The reporter tested it anyway, named the agent “Bob” and handed over access to their accounts.

Meta defends the product. “Muse is the first personal AI agent built for everyone and designed to be safe, secure and private – with built-in protections and user controls that put people in charge of how they use it,” a Meta spokesperson said. “Safety and security is a huge priority for us,” the spokesperson added, and said Muse went through extensive testing.

The ticket problem scales up

Experts expect the problems to look like the ones scalpers already cause. In 2024, some American fans of Taylor Swift flew to Europe to see her because resellers had pushed US ticket prices so high that a flight to an international concert cost less. Scalpers buy tickets to resell at a mark-up.

An agent gives anyone the same tool. Calli Schroeder, director of the AI and Human Rights Program at the Electronic Privacy Information Center (Epic), expects a sharp rise in bot activity. “There’s going to be a huge escalation of the problems we’re already having with bots,” she said.

The effects reach ordinary errands. Reservations at a hot new restaurant could become close to impossible to get. Appointments for passport or driver’s licence renewals in peak travel season could vanish too. Some people will probably hoard slots, booking five appointments just in case, since an agent makes that effortless.

Solutions exist. Society could drop “first come first served” and move to lotteries for scarce slots. That would change how much of daily life works. Schroeder sees little preparation. “I haven’t seen a lot of plans to address these things,” she said. “We’re just launching these tools and saying, ‘well, we’ll deal with the problems when they come up’.”

Meta says Muse asks permission before buying anything. According to the company, it is built to behave like a “reasonable, honest person”, one who would not buy every ticket to an event or refresh a page 500 times an hour.

Websites under strain

The reporter found Muse useful. Over a week, it messaged a seller on Facebook Marketplace with questions, ordered the reporter’s preferred dental floss and negotiated a $31 (£23) discount on a software subscription.

Now picture millions of agents doing this at once, on tasks that might take a person weeks. Schroeder asked what that does to the sites on the receiving end. “What happens if bots send 600 inquiries to a website a day, when normal humans might only send two?” she said. By our arithmetic, that is 300 times the normal load from a single visitor. “Businesses and individuals are going to have a lot to deal with.”

Web businesses already face pressure. Google and chatbots now answer many questions directly, so people visit fewer websites. Robots do not click ads or buy subscriptions, and the income those visits once produced is shrinking. Agents are expected to deepen the problem.

One analysis found that web traffic from bots rose 124% in the year to June 2026. Some websites and services are struggling because they were not built for that load.

Meta’s spokesperson said Muse completes tasks while respecting the interests of websites.

Whose side is the agent on?

Personal risks sit alongside the public ones. “If you’re empowering an agent to make things like purchasing decisions, or choices about taste and preferences, you’re opening yourself up to being exploited,” Schroeder said.

She gave examples. If Muse plans a holiday, a user has no way to check whether it found the best deal or picked flights and hotels that benefit Meta’s business partners. If it recommends music, the user cannot tell whether the picks come from their taste or from artists who signed deals with Meta.

Meta says Muse’s protections and user controls put people “absolutely in charge”, and that Muse “behaves like a personal assistant acting for a single person” and follows ethical guidelines meant to protect users. Schroeder has read the terms of service. She said they contain no guarantee that the app will act in the user’s favour.

Proposals for new rules

Ramesh Raskar, an associate professor at the Massachusetts Institute of Technology who studies AI agents, uses a driving comparison for the current situation. “Imagine there are no rules of the road. And you release billions of cars – the AI agents – and you just let them drive through playgrounds, hitting kids. That’s where we are,” he said.

Raskar is among the researchers designing an internet that works for agents, businesses and people alike. He argues that regulators need an approach built for agents. “Think about the models like an engine. The agents are the cars, and that’s what we need to regulate,” he said. “We need to establish the rules of the road: windshields, brakes, traffic lights and so on.”

The AI industry is developing protocols and standards that let bots connect directly to other services in a cooperative way. Some companies are building systems that would charge AIs a fee to scrape websites. Regulation could require agents to serve their users’ best interests.

There are early examples. A few restaurant reservation platforms have banned people for AI misuse. The UK has rewritten the rules for booking driving tests, in part to combat bots.

Raskar remains optimistic. “Agents could unlock so much investment, innovation and value,” he said, as long as the new rules do not hand any company an unfair advantage. In the meantime, people who use agents pay with personal data.

What Muse holds, and what Meta promises

The reporter has used the same Gmail address for 21 years. It is the login for hundreds of accounts. It holds medical test results, contracts, legal documents, family conversations, receipts and financial information. It also holds love letters from an ex-girlfriend, who gave permission before the account was connected. Muse also suggested connecting bank accounts. The reporter declined and did not let the agent loose on the hard drive.

Meta makes explicit privacy promises. The company says it will not connect any data Muse collects to its advertising systems. Special systems are meant to keep the AI from seeing passwords or payment methods. When a user connects Gmail, the agent asks whether it should scan the whole inbox or read only messages related to specific tasks.

There is a catch, according to Schroeder. By default, Meta uses Muse data to train new AI models. She said data built into a model cannot be removed, and that AIs can sometimes be tricked into revealing training data. Meta says it “sanitises” data to strip out personally identifiable information before training, and that users can opt out with a setting.

Wardle does not take those assurances at face value. Soon after launch he found a critical vulnerability. “This was literally 20 minutes of me poking at the app, and it just, like, fell over,” he said. With a simple hack, he said, an attacker could have taken over Muse and all of its data, and even controlled other connected devices such as a phone or a smart lock.

Meta fixed the flaw immediately. Wardle says the oversight still leaves him unable to trust the company’s privacy and safety claims. “These bugs were trivial to discover,” he said. “If they were willing to ship something that’s security was not well vetted, it doesn’t give me a warm fuzzy about their intentions.”

A Meta spokesperson disputes that view and said Muse was delayed for months for further privacy and security testing.

The tester’s decision

The reporter spent a lot of time with Bob and found the agent useful and enjoyable. After finishing the article, the reporter revoked Muse’s Gmail access and asked the app to erase everything it had collected.

The reporter’s reason was simple: “In the end, the fear won out.”

Sources: BBC News reporting on Meta’s Muse AI agent; comments from Patrick Wardle (Objective-See), Calli Schroeder (Electronic Privacy Information Center), Ramesh Raskar (MIT); statements from a Meta spokesperson.

Tech

Trump Renames AI “Super Intelligence” in Executive Order as Calls for Regulation Grow

By George Mensah 4 min read

President Donald Trump signed an executive order on Tuesday, Sept. 29, 2026, that renames artificial intelligence “super intelligence” across the federal government. The White House says the new term better describes what the technology can do. The order lands as critics press Washington for stricter limits on how fast AI develops.

What the order says

The executive order argues that current systems do “much more than imitate or automate discrete aspects of human intelligence.” It goes further in its central passage. “As these capabilities continue to improve, they increasingly represent not merely artificial intelligence, but a new era of Super Intelligence,” the text reads.

It adds that federal terminology “should reflect the transformative capabilities of these technologies and the limitless opportunities they create for the American people.”

Trump spoke to reporters after signing. “It’s not artificial, we all agree on that,” he said.

What agencies must do now

Every federal agency has to use the new term, or its short form “SI,” when it talks about the technology in public. That covers public communications, websites, reports and policy documents. If your local agency publishes an AI guidance page, expect it to change.

The order also gives Michael Kratsios, director of the Office of Science and Technology Policy, a defining role. He will decide whether the official definition of “super intelligence” should be modified or expanded. The order does not set a deadline for that decision.

A term that already means something else

The rename creates a vocabulary problem. In the AI field, super intelligence already refers to a specific kind of system, one that exceeds human cognitive ability in virtually every area of thinking. Nobody has built one. Researchers treat it as a future possibility, and much of the safety debate centers on it.

Under the order, federal documents will apply that label to chatbots, coding assistants and image generators that exist today. A reader who sees “SI” in a government report may assume the government is describing something far more advanced than what companies actually sell. Kratsios’s authority to modify the definition could narrow that gap, or it could widen it.

Timing and the push against regulation

The order follows a week of similar messaging. Trump began using the term at the U.N. General Assembly last week, where he pushed back on calls for tighter rules on the industry. He told world leaders that tech executives would build the right guardrails into their own models.

Concerns have grown since then. Worries about AI replacing workers keep rising. Recent reporting has also described rogue agents linked to a security breach involving Australia’s prime minister, and AI agents that accessed U.S. government websites. Some systems have also been used to start cyberattacks.

Trump has repeatedly called whistleblower warnings about weak oversight overblown and a “hoax.” He has said he will not slow AI growth. In his view, keeping American dominance in the technology is a national security matter.

The industry’s own safeguard

On the same day, tech executives signed a “morally binding” constitution on AI at the White House. Its terms ask companies to hire an independent external auditor. The auditor would check that models are “operating as intended.”

The document also asks companies to set up internal controls meant to stop models from hacking systems. A team would monitor those controls. That team would answer to an independent committee of the company’s board.

The wording matters here. “Morally binding” describes an obligation companies accept by choice. The reporting on the document does not describe fines, penalties or a government body that could enforce it. Whether outside auditors get real access to model internals, and what happens if one finds a problem, are open questions.

What the two actions have in common

The order and the constitution came out the same day, and they share a theme. Both keep the government’s role limited. The order changes what officials call the technology. The constitution leaves safety checks largely in company hands.

Supporters of that approach say it keeps American firms moving fast against foreign competitors. They argue that rigid rules written now could be out of date within a year. Critics say voluntary pledges have a weak record in other industries, and that a stronger name for the technology may make the public less cautious about it.

Neither side has settled the argument. What is clear is the direction of policy. The administration is choosing branding and industry commitments over new binding rules, at a moment when the documented incidents involving AI agents are piling up.

What happens next

Three things are worth watching over the coming weeks.

  • Kratsios’s definition. Any change to the official meaning of “super intelligence” will show how the administration wants the term understood.
  • Agency compliance. Federal sites and reports should begin switching to “SI” now that the order requires it.
  • The auditor provision. The industry constitution only matters if independent auditors are named, given access and allowed to publish what they find.

Congress has not yet responded to the order, and no agency has published a compliance timeline. Until Kratsios acts on the definition, “super intelligence” will mean one thing to researchers and something looser in federal paperwork.

ADVERTISEMENT
Scroll to Top